 LMS
 Reels Series
How Much Does SOC 2 Compliance Cost in Australia in 2026?
Introduction
Understanding the SOC 2 compliance cost in Australia is important for businesses that want to demonstrate strong information security and build trust with customers. As Australian SaaS companies, cloud service providers, fintech businesses, and technology organisations work with enterprise clients, demonstrating effective security controls can help them compete for new business opportunities.
SOC 2 compliance involves assessing how an organisation protects customer data and manages security risks. The overall cost depends on several factors, including company size, system complexity, existing security controls, audit type, and the level of external support required.
In 2026, businesses should consider both the initial investment and ongoing expenses associated with maintaining compliance. With appropriate planning and expert guidance from CyberSapiens, organisations can understand their requirements, manage preparation costs, and establish a practical path towards SOC 2 readiness and auditing.
What Is SOC 2 Compliance?
SOC 2 is an assurance framework developed by the American Institute of Certified Public Accountants (AICPA). It evaluates controls relevant to the Trust Services Criteria, helping organisations demonstrate how they protect information and operate their systems.
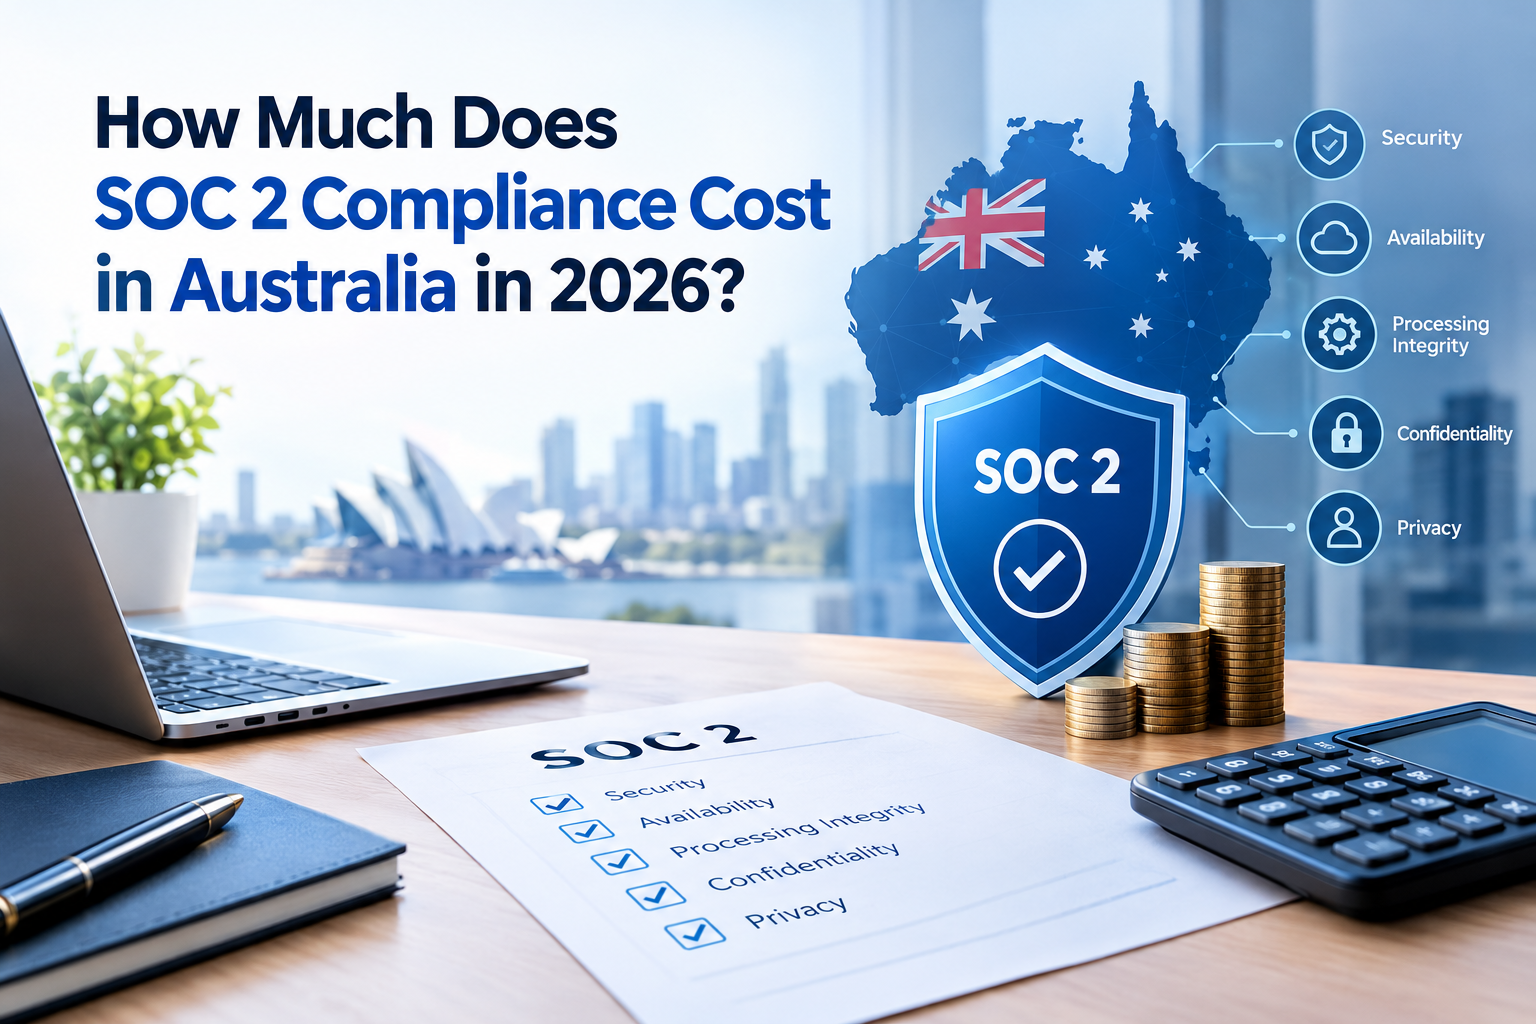
The five Trust Services Criteria are:
-
Security: Protecting systems and information against unauthorised access.
-
Availability: Maintaining systems and services according to agreed commitments.
-
Processing Integrity: Ensuring system processing is complete, valid, accurate, and timely.
-
Confidentiality: Protecting information designated as confidential.
-
Privacy: Managing personal information according to applicable privacy commitments.
Security is the common foundation of a SOC 2 examination. Other criteria are included depending on the services offered, customer expectations, and business requirements.
SOC 2 is not a certification in the same sense as ISO 27001. Instead, an independent licensed CPA firm conducts an examination and issues a SOC 2 report.
How Much Does SOC 2 Compliance Cost in Australia in 2026?
The cost varies significantly between organisations. There is no single fixed price that applies to every Australian business because the scope, current security maturity, and audit requirements differ.
The total budget may include:
-
SOC 2 readiness assessments and gap analysis.
-
Security policies and documentation.
-
Risk assessments and control implementation.
-
Compliance automation software.
-
Technical security improvements.
-
Independent audit fees.
-
Staff training and ongoing monitoring.
A business with established security processes may require less preparation than a startup building its security programme from the beginning. For an accurate estimate, organisations should request a tailored quote based on their scope and audit objectives rather than relying on a universal price.
Key Factors That Affect SOC 2 Compliance Cost in Australia
Several factors influence the total cost of a SOC 2 programme.
1. SOC 2 Type 1 vs Type 2
The type of report is one of the most important cost considerations.
-
SOC 2 Type 1: Evaluates whether relevant controls are suitably designed at a specific point in time.
-
SOC 2 Type 2: Evaluates control design and operating effectiveness over a defined observation period, often six to twelve months.
Type 2 generally requires more evidence collection and testing over time, which can increase the audit fee and internal workload.
2. Business Size and Complexity
Small businesses with a single product and limited infrastructure may have fewer systems and controls to assess. Larger organisations with multiple applications, cloud environments, teams, and business locations often require more extensive testing.
The complexity of your technology environment can therefore affect both preparation time and auditor fees.
3. Existing Security Controls
Businesses that already maintain documented security policies, access controls, incident response procedures, and risk assessments may need less remediation.
Organisations starting from scratch may need additional support to implement controls, document procedures, and establish evidence collection processes before the audit.
4. Compliance Software and Technical Testing
Compliance automation platforms can help manage evidence, monitor controls, and track remediation tasks. However, subscription fees can add to the overall budget.
Additional technical work, such as vulnerability assessments and penetration testing, may also be required or recommended depending on your risks, customer expectations, and audit scope.
5. Number of Trust Services Criteria
Security is the foundation of SOC 2. Adding Availability, Processing Integrity, Confidentiality, or Privacy can increase the scope of work, particularly when these criteria require additional controls and evidence.
Businesses should select criteria based on their services, contractual obligations, and customer requirements rather than including every category unnecessarily.
Estimated SOC 2 Compliance Cost in Australia
CyberSapiens publishes the following indicative first-year pricing ranges for its consultancy and audit-partner model. Actual pricing depends on the business's scope, size, and security maturity.
|
Business type |
Indicative cost (AUD) |
|---|---|
|
Early-stage startups |
$8,000–$20,000 |
|
Small to mid-sized SaaS businesses |
$12,000–$30,000 |
|
Larger or complex environments |
$30,000+ |
These are provider-published indicative ranges, not guaranteed prices or universal market rates. Confirm whether a quote includes the independent examination, readiness support, software, remediation, and applicable taxes. The scope and inclusions can make two quotes difficult to compare.
How to Reduce SOC 2 Compliance Costs
Australian businesses can control expenses by following a structured approach.
-
Define the scope early: Identify the services, systems, and customer data included in the examination.
-
Conduct a readiness assessment: Identify control gaps before engaging the auditor for the formal examination.
-
Reuse existing controls: Map relevant security processes and evidence to SOC 2 requirements where appropriate.
-
Automate evidence collection: Use suitable tools to reduce repetitive manual work.
-
Assign internal responsibilities: Give clear ownership of access reviews, risk assessments, policies, and incident response.
-
Compare audit proposals: Review the auditor's qualifications, scope, deliverables, observation period, and fees.
A practical compliance roadmap helps businesses avoid unnecessary spending while building sustainable security processes.
Why Choose CyberSapiens for SOC 2 Compliance?
CyberSapiens helps businesses navigate cybersecurity and compliance requirements with solutions tailored to their operational needs. For organisations planning SOC 2, suitable support can include readiness assessments, gap analysis, control implementation guidance, policy documentation, and audit preparation.
CyberSapiens can help Australian businesses understand their compliance gaps, organise evidence, and plan remediation activities before the formal examination. Businesses should confirm the precise services included in their engagement and ensure the final SOC 2 report is issued by an appropriately qualified independent CPA firm.
Whether you are a startup preparing for your first customer security review or an established technology provider expanding into international markets, a structured compliance strategy can make the process more manageable.
Explore the CyberSapiens SOC 2 cost guide to learn more about pricing considerations and available support.
Frequently Asked Questions (FAQs)
1. How much does SOC 2 compliance cost in Australia in 2026?
The cost depends on company size, audit type, security maturity, and service scope. CyberSapiens publishes indicative pricing from AUD $8,000 for some early-stage startups, while larger and more complex environments can cost AUD $30,000 or more. Request a tailored quote to confirm the full scope.
2. Is SOC 2 Type 2 more expensive than Type 1?
Generally, yes. Type 2 requires evidence of controls operating effectively over an observation period, which adds testing and monitoring work compared with Type 1.
3. How long does SOC 2 compliance take?
The timeline depends on existing security controls and the complexity of the business. Preparation may take weeks or months, while a Type 2 examination also requires an observation period commonly lasting six to twelve months.
4. Is SOC 2 mandatory for Australian businesses?
SOC 2 is not a universal legal requirement for Australian businesses. However, enterprise customers and international clients may request a SOC 2 report as part of their vendor security assessment.
5. Can a small business afford SOC 2 compliance?
Yes. Small businesses can start by defining a focused scope, addressing critical security gaps, reusing existing controls, and choosing an appropriate audit provider. Costs should be evaluated against customer requirements and expected business benefits.
6. Does ISO 27001 replace SOC 2?
No. ISO 27001 certification and SOC 2 reports serve different purposes. Existing ISO 27001 controls may support SOC 2 preparation, but customers requesting a SOC 2 report may still require an independent SOC 2 examination.
7. What is included in SOC 2 compliance pricing?
Depending on the proposal, pricing may include readiness assessments, policies, control implementation, compliance software, technical testing, internal staff effort, and independent audit fees. Always confirm inclusions before signing an agreement.
Conclusion
The SOC 2 compliance cost in Australia in 2026 depends on your audit objectives, existing controls, business complexity, and preparation requirements. Understanding these factors helps you create a realistic budget and avoid unexpected expenses.
With careful planning and support from CyberSapiens, Australian businesses can strengthen information security, prepare for independent examinations, and build customer confidence. Start by assessing your current security posture, defining your audit scope, and obtaining a detailed quote that matches your business requirements.
 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek